Architecture at a glance
Five layers, left to right: your facility assets, your control and field systems, the connection path, the Enerzyz cloud, and the people using it. Your BMS, SCADA, IoT sensors and metering networks stay where they are — Enerzyz reads from them over standard protocols. The command path is bidirectional: telemetry flows up, supervisory set-points flow back down through your BMS, and every action is logged with its justification.
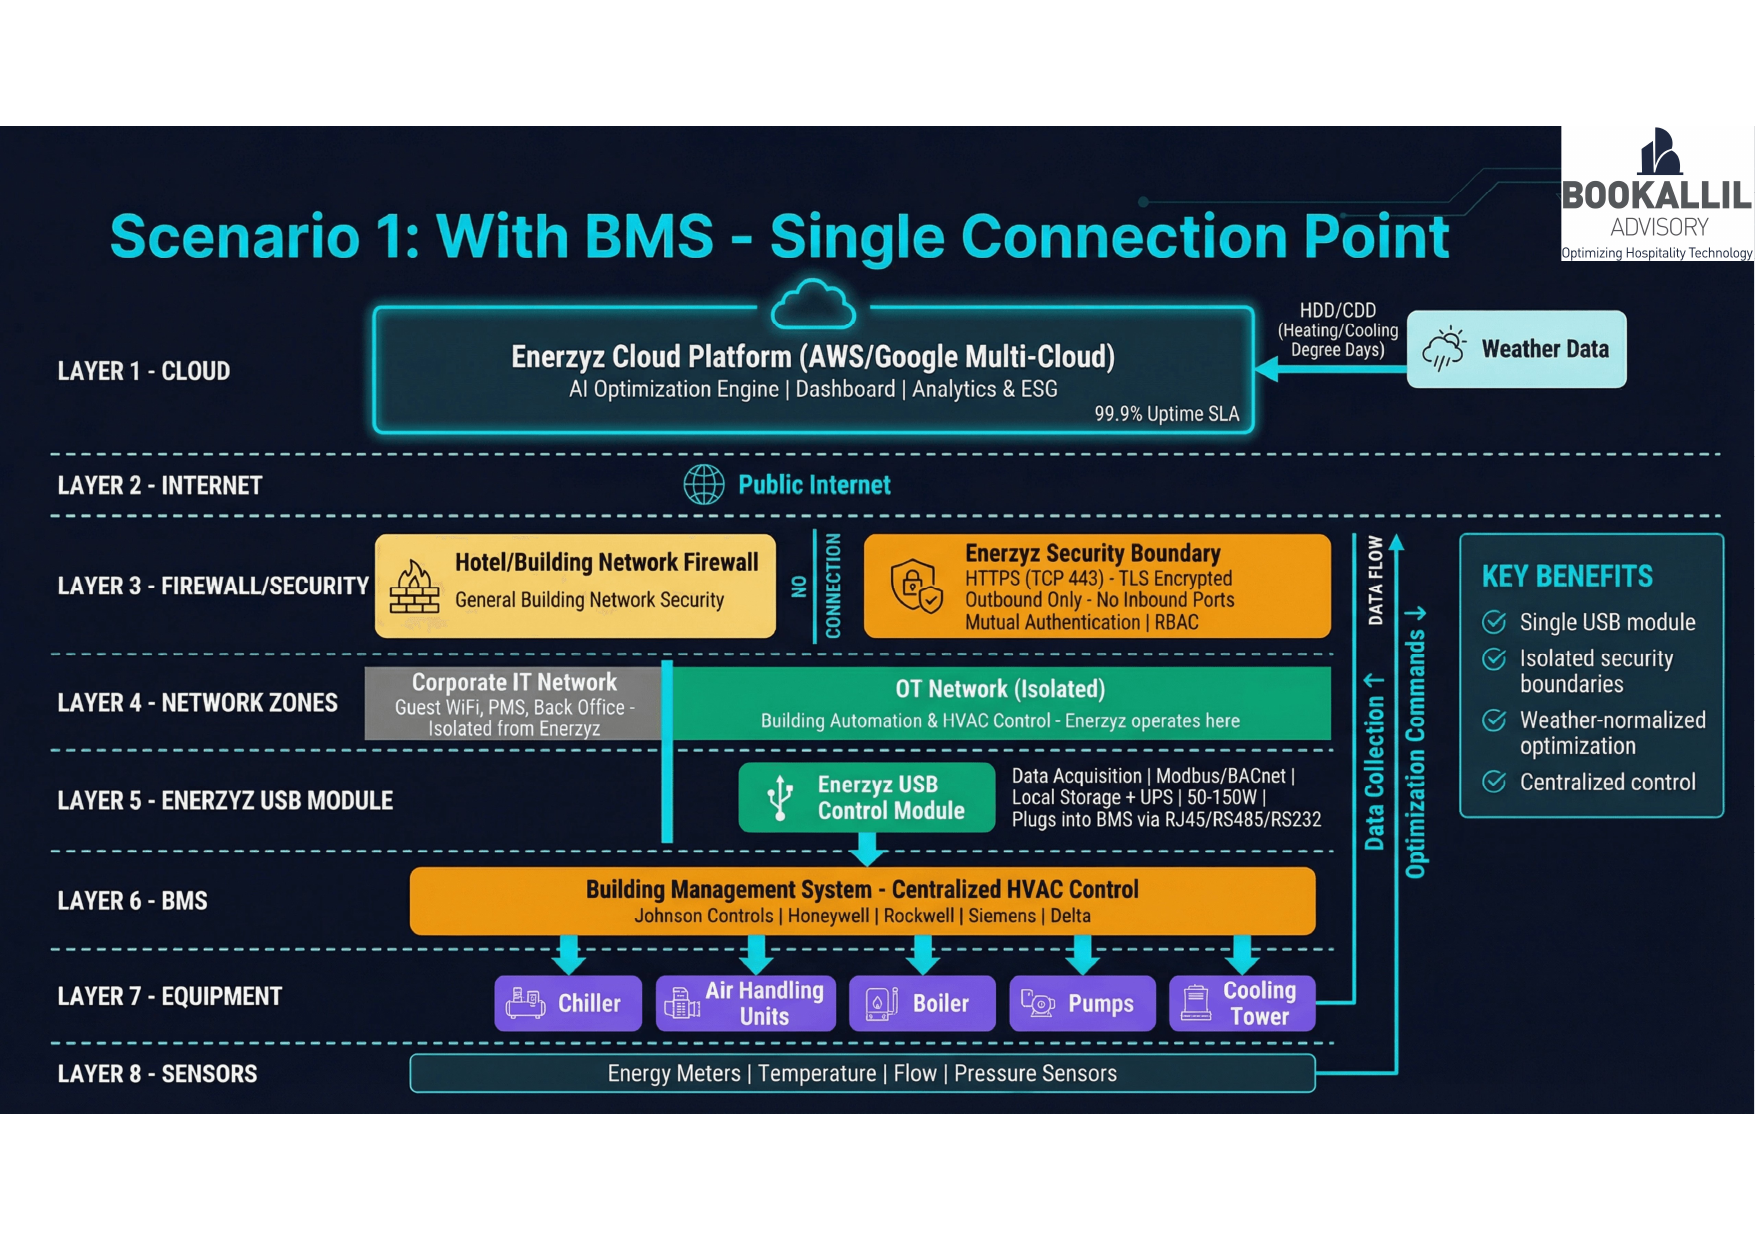
Scroll the diagram sideways to read it in full.
Four ways to connect a facility
The same Enerzyz cloud, reached by whichever path suits the site. Unified API needs no hardware: Enerzyz connects to your BMS vendor cloud. Edge Mini is a small dongle on your BMS network. Edge Pro is a compact gateway that keeps your BMS network separate. Edge Max is for sites without internet, with a USB modem; its availability is confirmed per country. The paths combine on one site, and the choice is made with you, site by site. The diagram shows Unified API, Edge Mini and Edge Max; Edge Pro is outbound-only in the same way. Your Full Facility Assessment identifies which path applies.
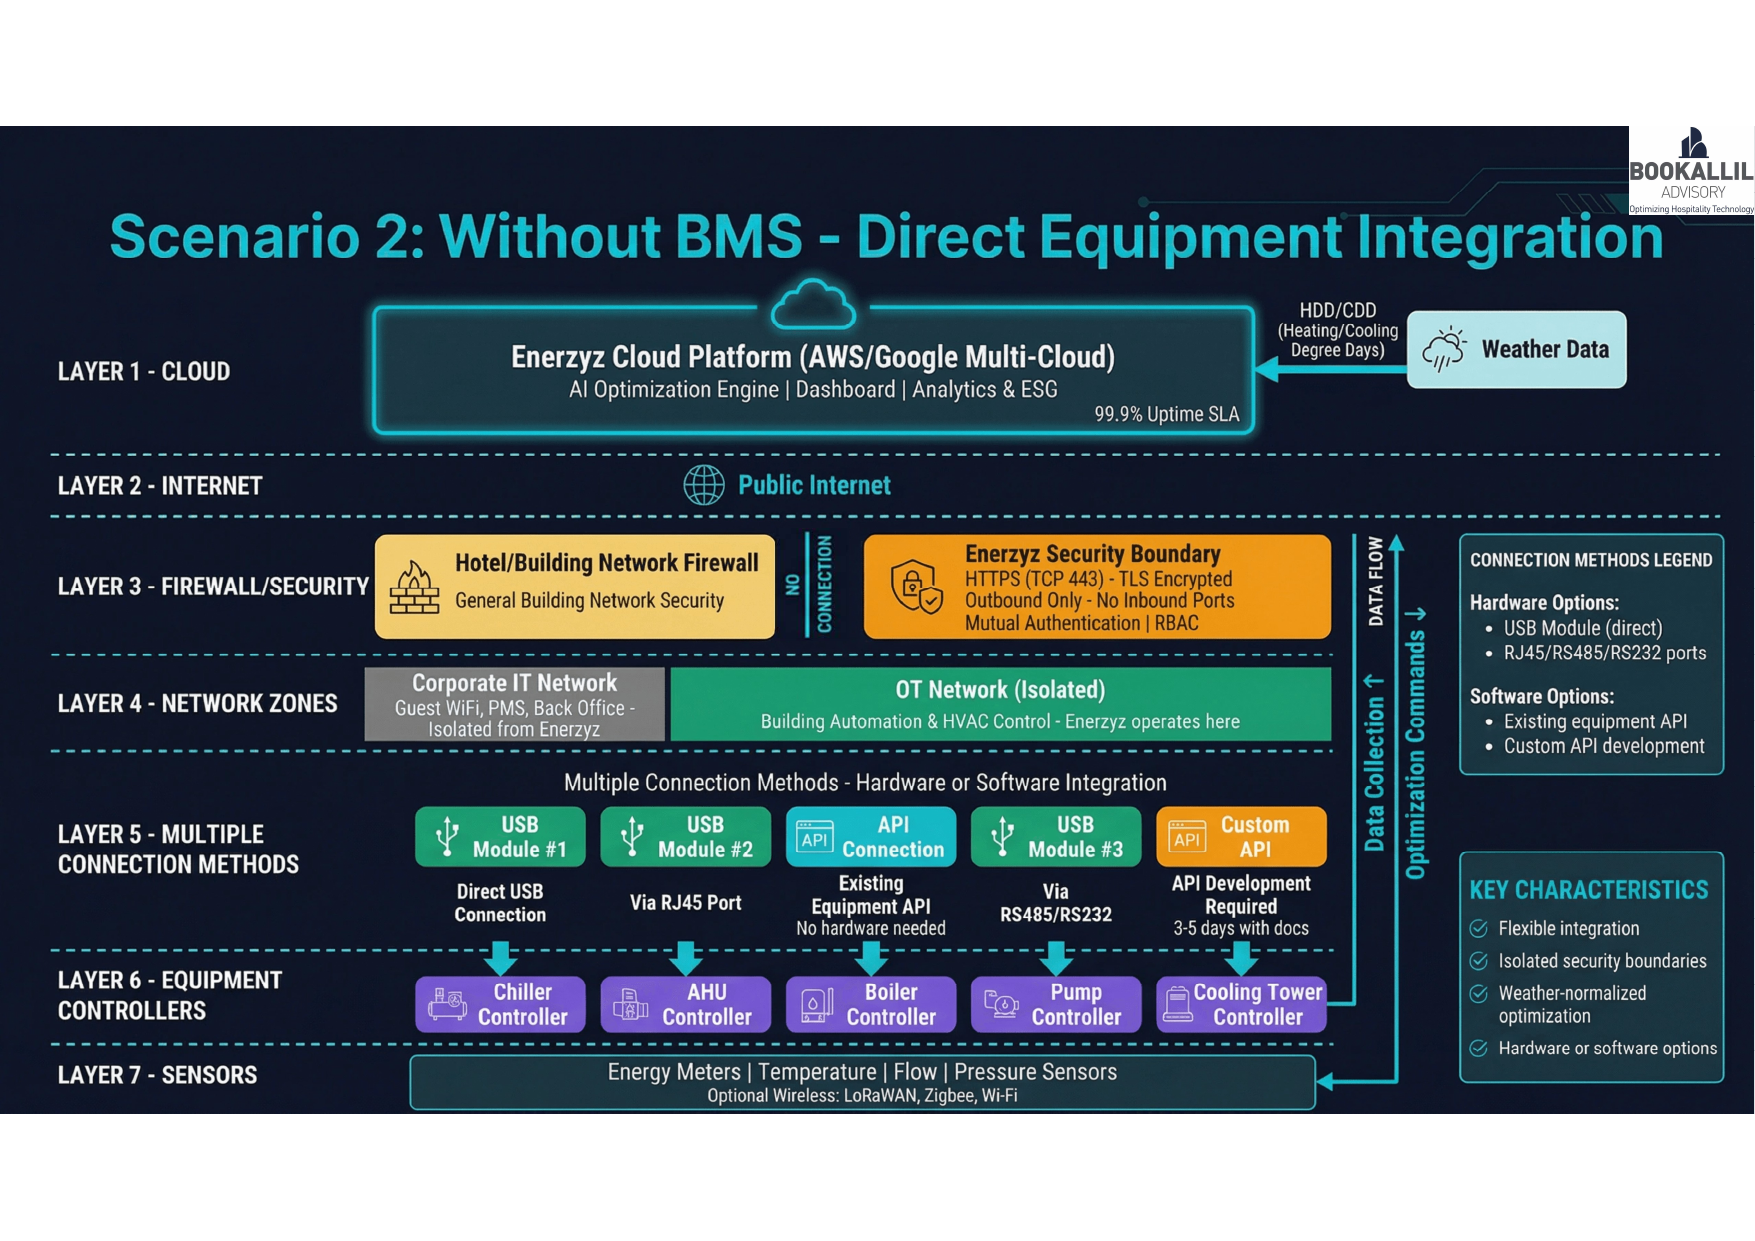
Scroll the diagram sideways to read it in full.
Unified API approach
The zero-hardware path. Enerzyz connects directly to your BMS vendor cloud, OEM portal or IoT platform over secure APIs using REST, MQTT or OPC-UA over TLS, authenticated with API keys or OAuth. Nothing is installed at the property, no site visit is required and there is no facility IT dependency. Typically live within hours. This is the right path when your BMS or assets are already cloud-connected.
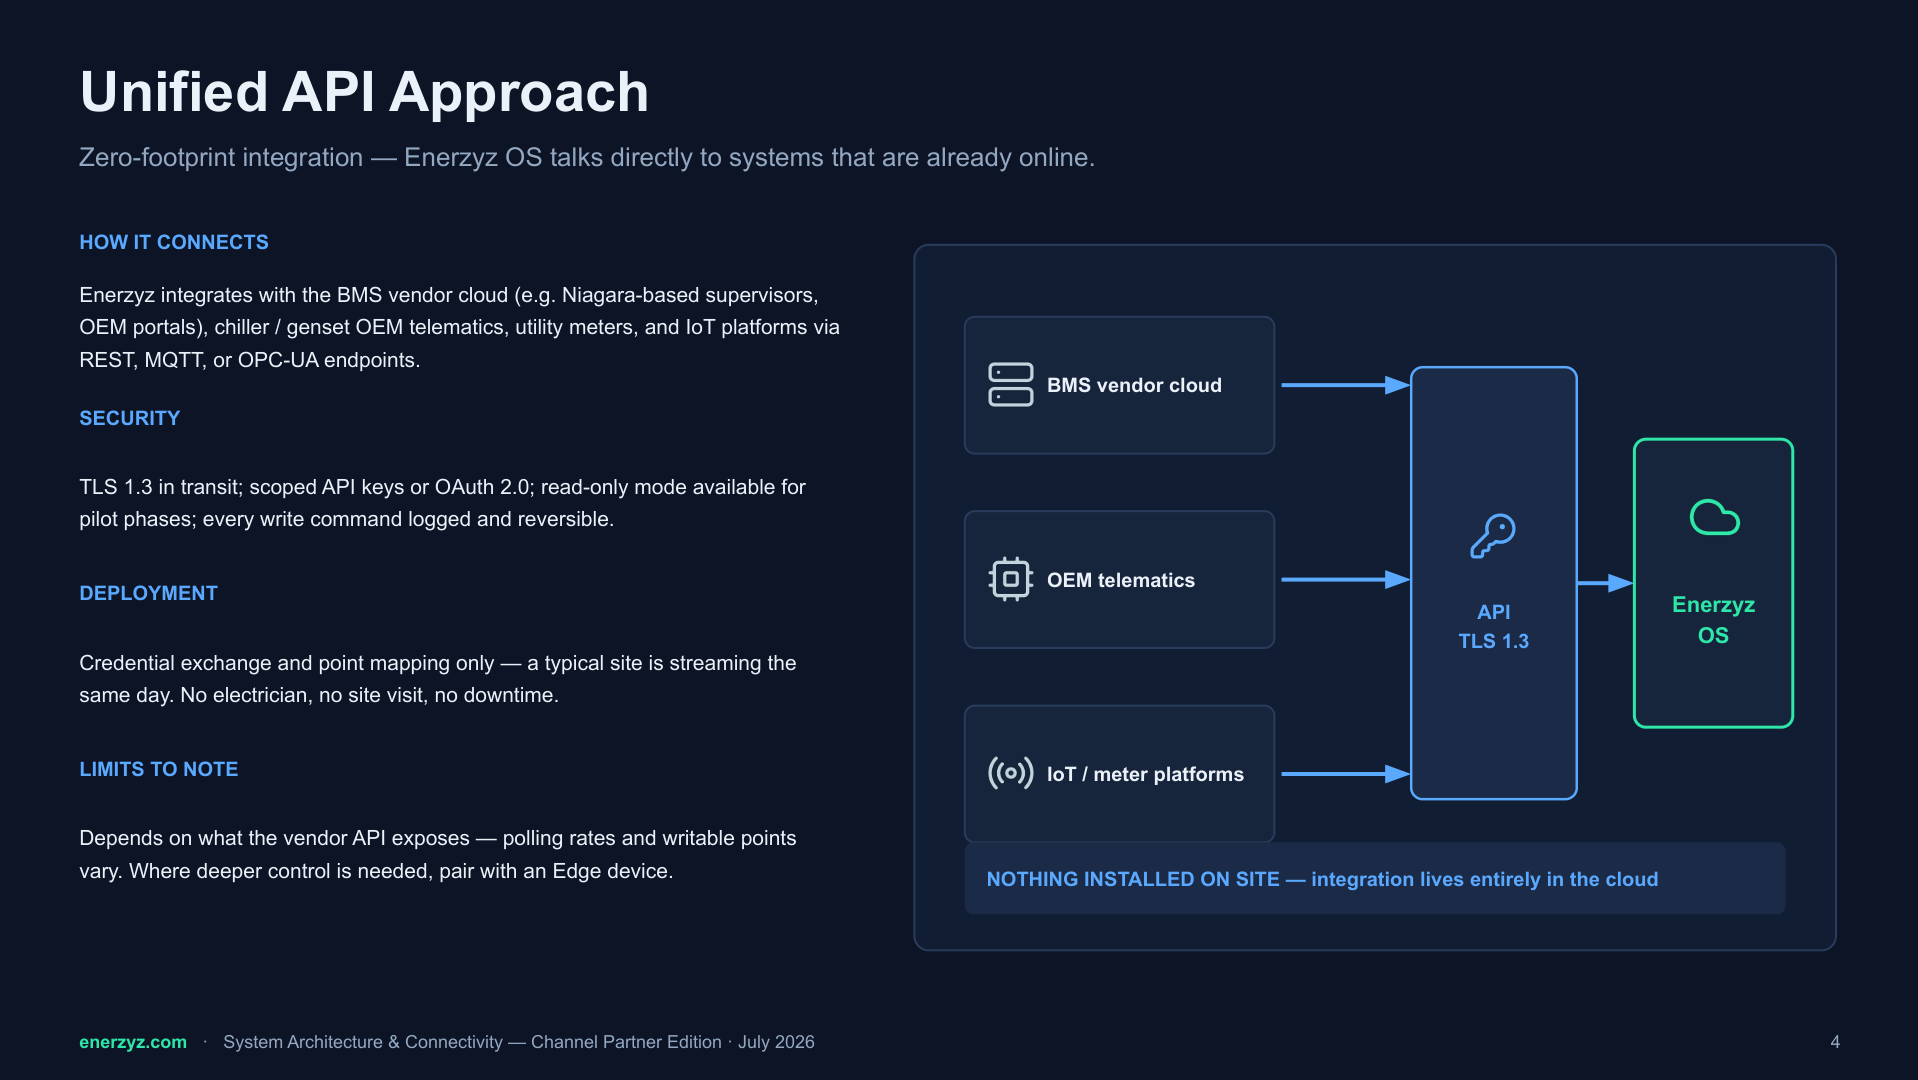
Scroll the diagram sideways to read it in full.
Enerzyz Edge Mini
A pocket-size dongle that clips in beside your BMS panel or network switch — no rack space and no enclosure work. A single RJ45 into the BMS/OT network, powered by USB-C or PoE over that same cable, auto-discovering BACnet/IP and Modbus TCP devices on the segment. Connectivity is outbound-only over TLS 443: no inbound rules are required at your firewall, no VPN. If the link drops, the site keeps running and the Mini resynchronises on reconnect.
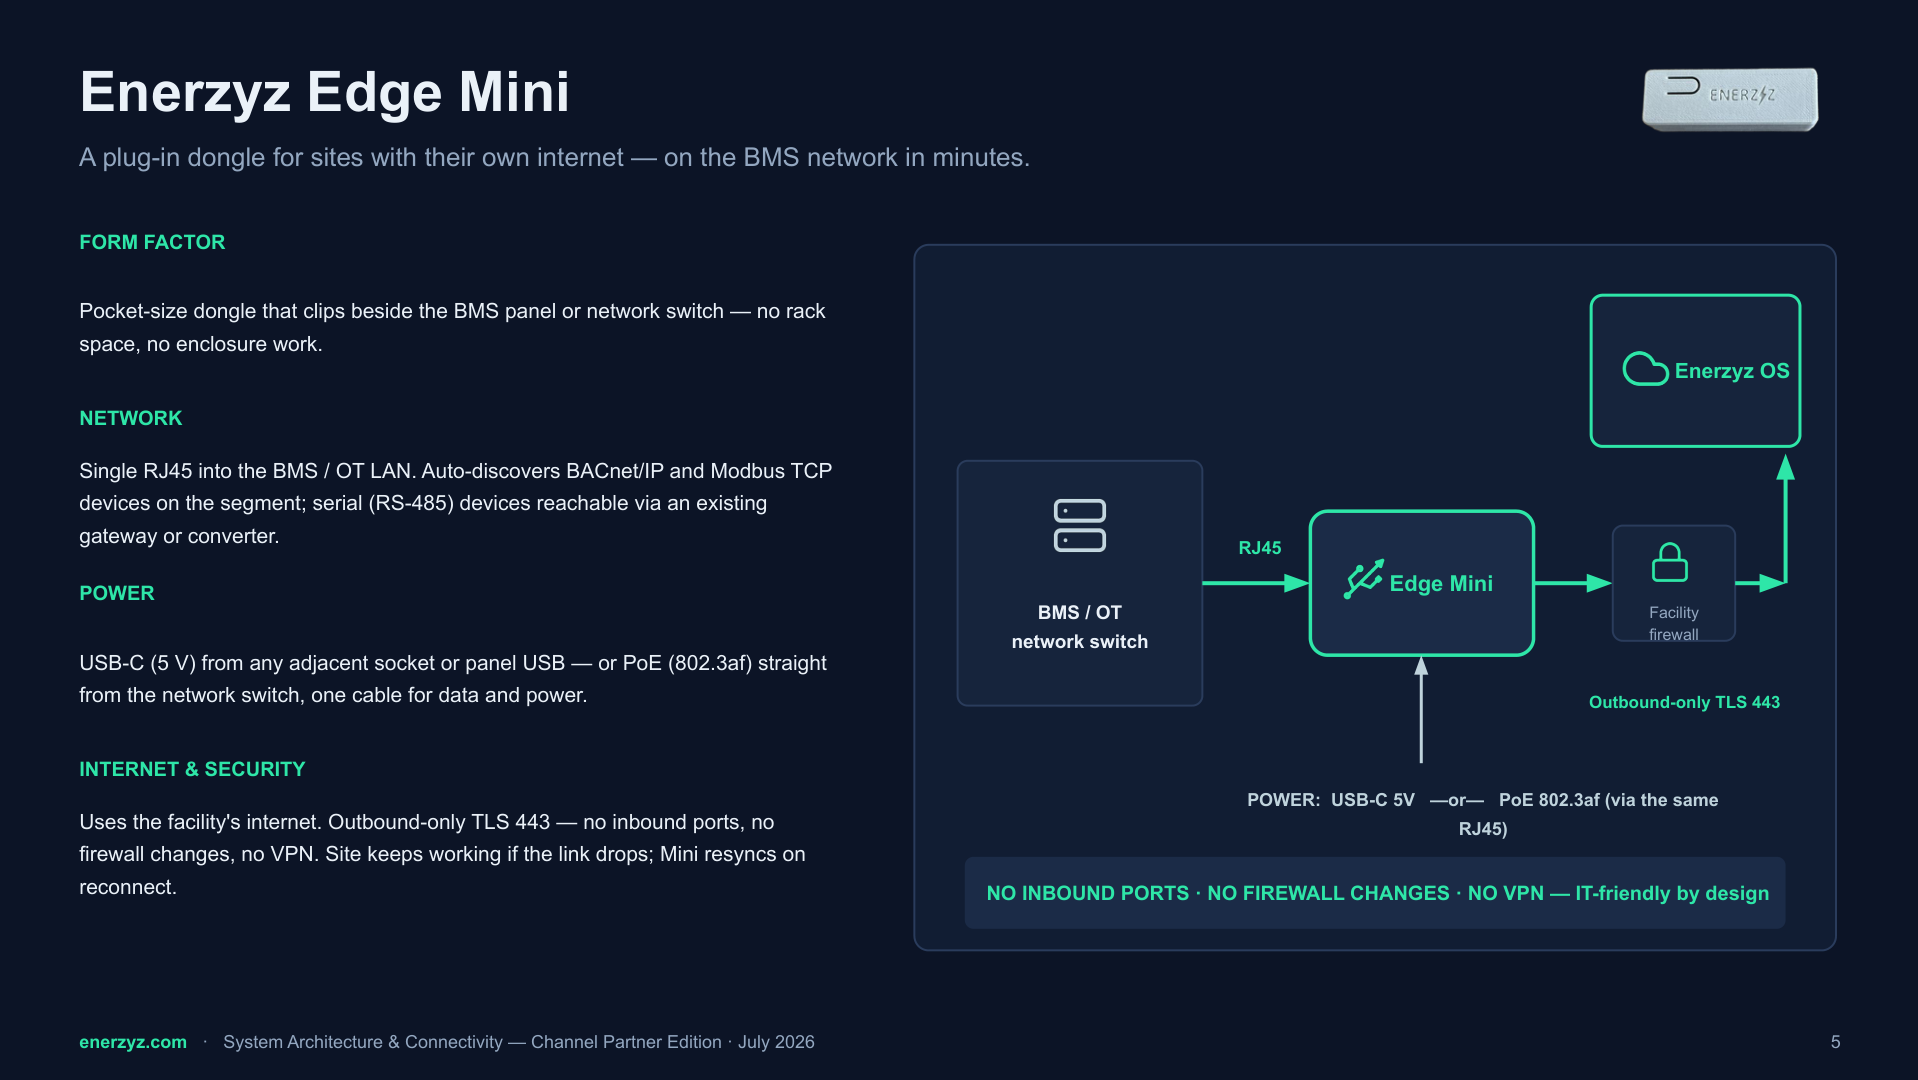
Scroll the diagram sideways to read it in full.
Enerzyz Edge Max
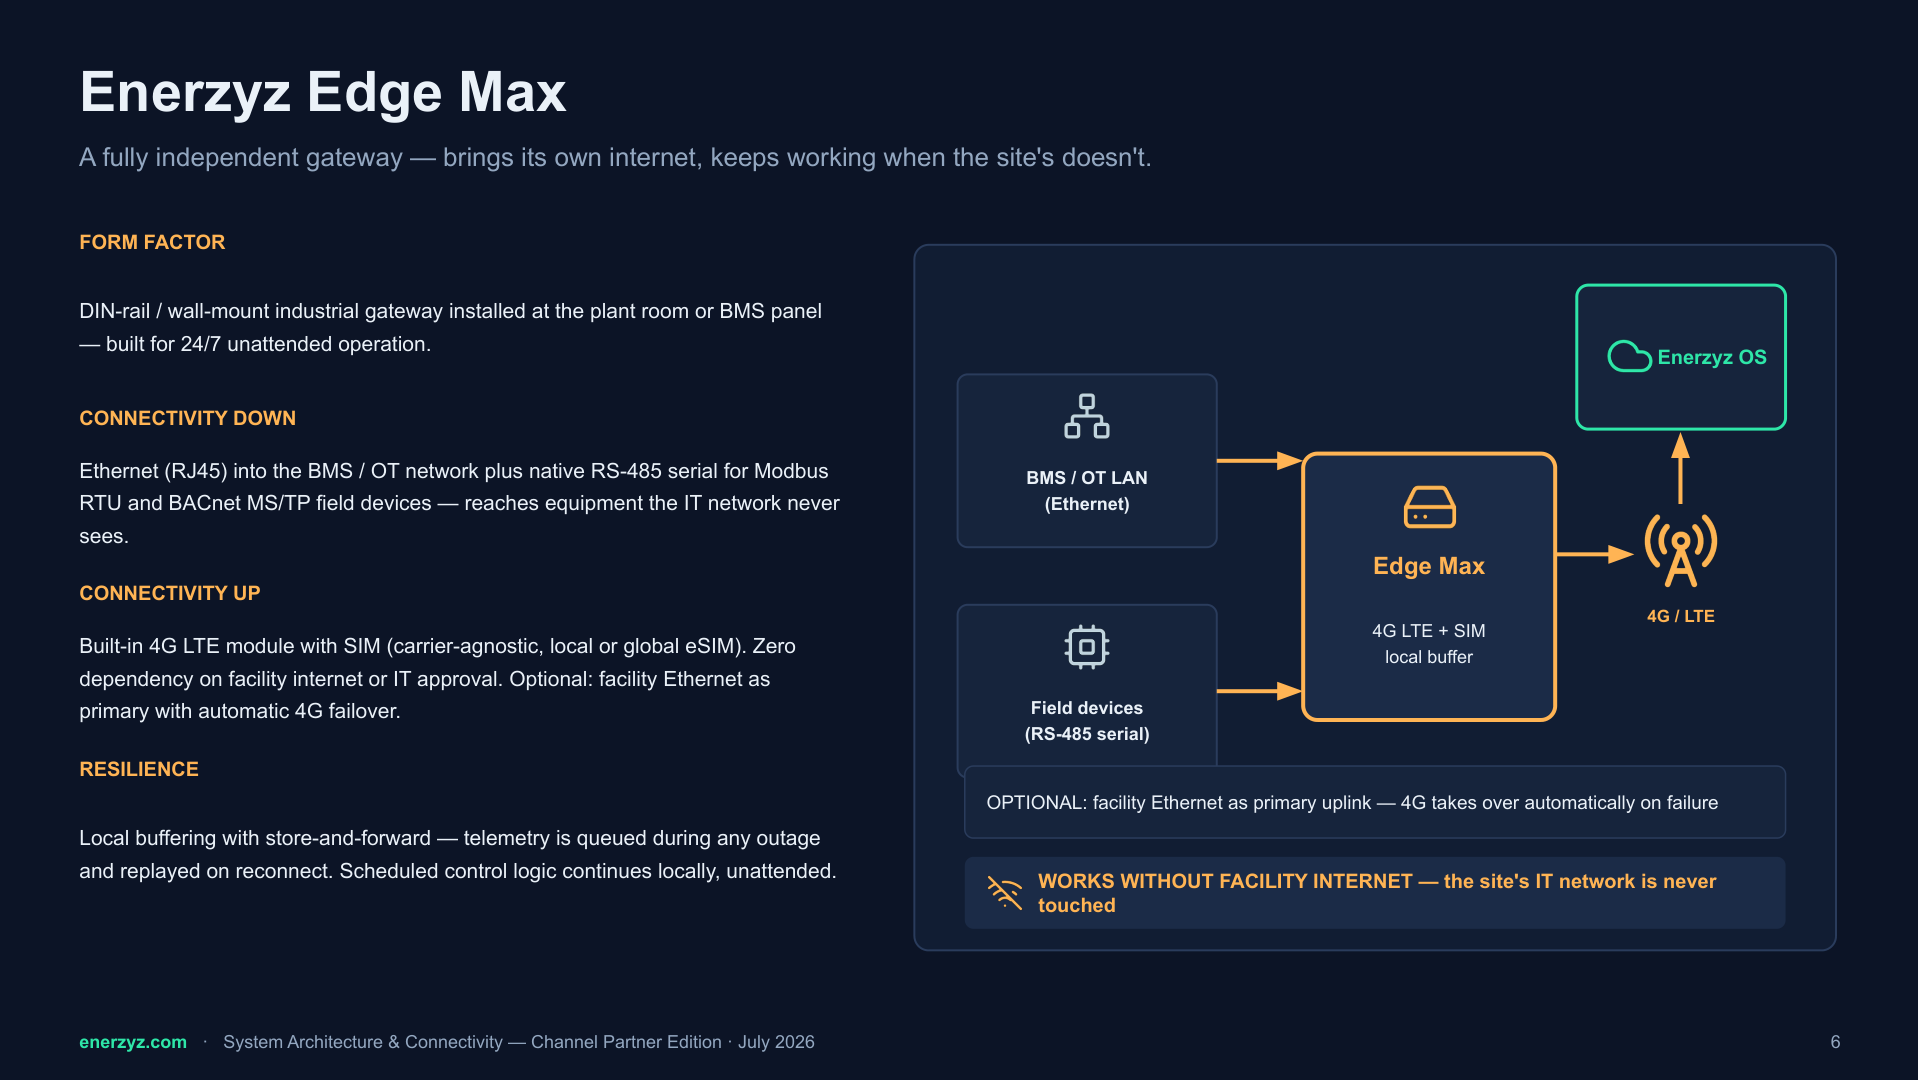
A self-contained industrial gateway with its own 4G LTE module and SIM, mounted on DIN rail or a wall, and sitting on the OT VLAN. It runs with zero dependency on facility IT — useful where there is no internet, where policy prevents connecting new devices, or at remote and critical sites. It reaches field devices over Ethernet and RS-485, and buffers locally then forwards on recovery if connectivity is interrupted.
Scroll the diagram sideways to read it in full.
Connectivity options, side by side
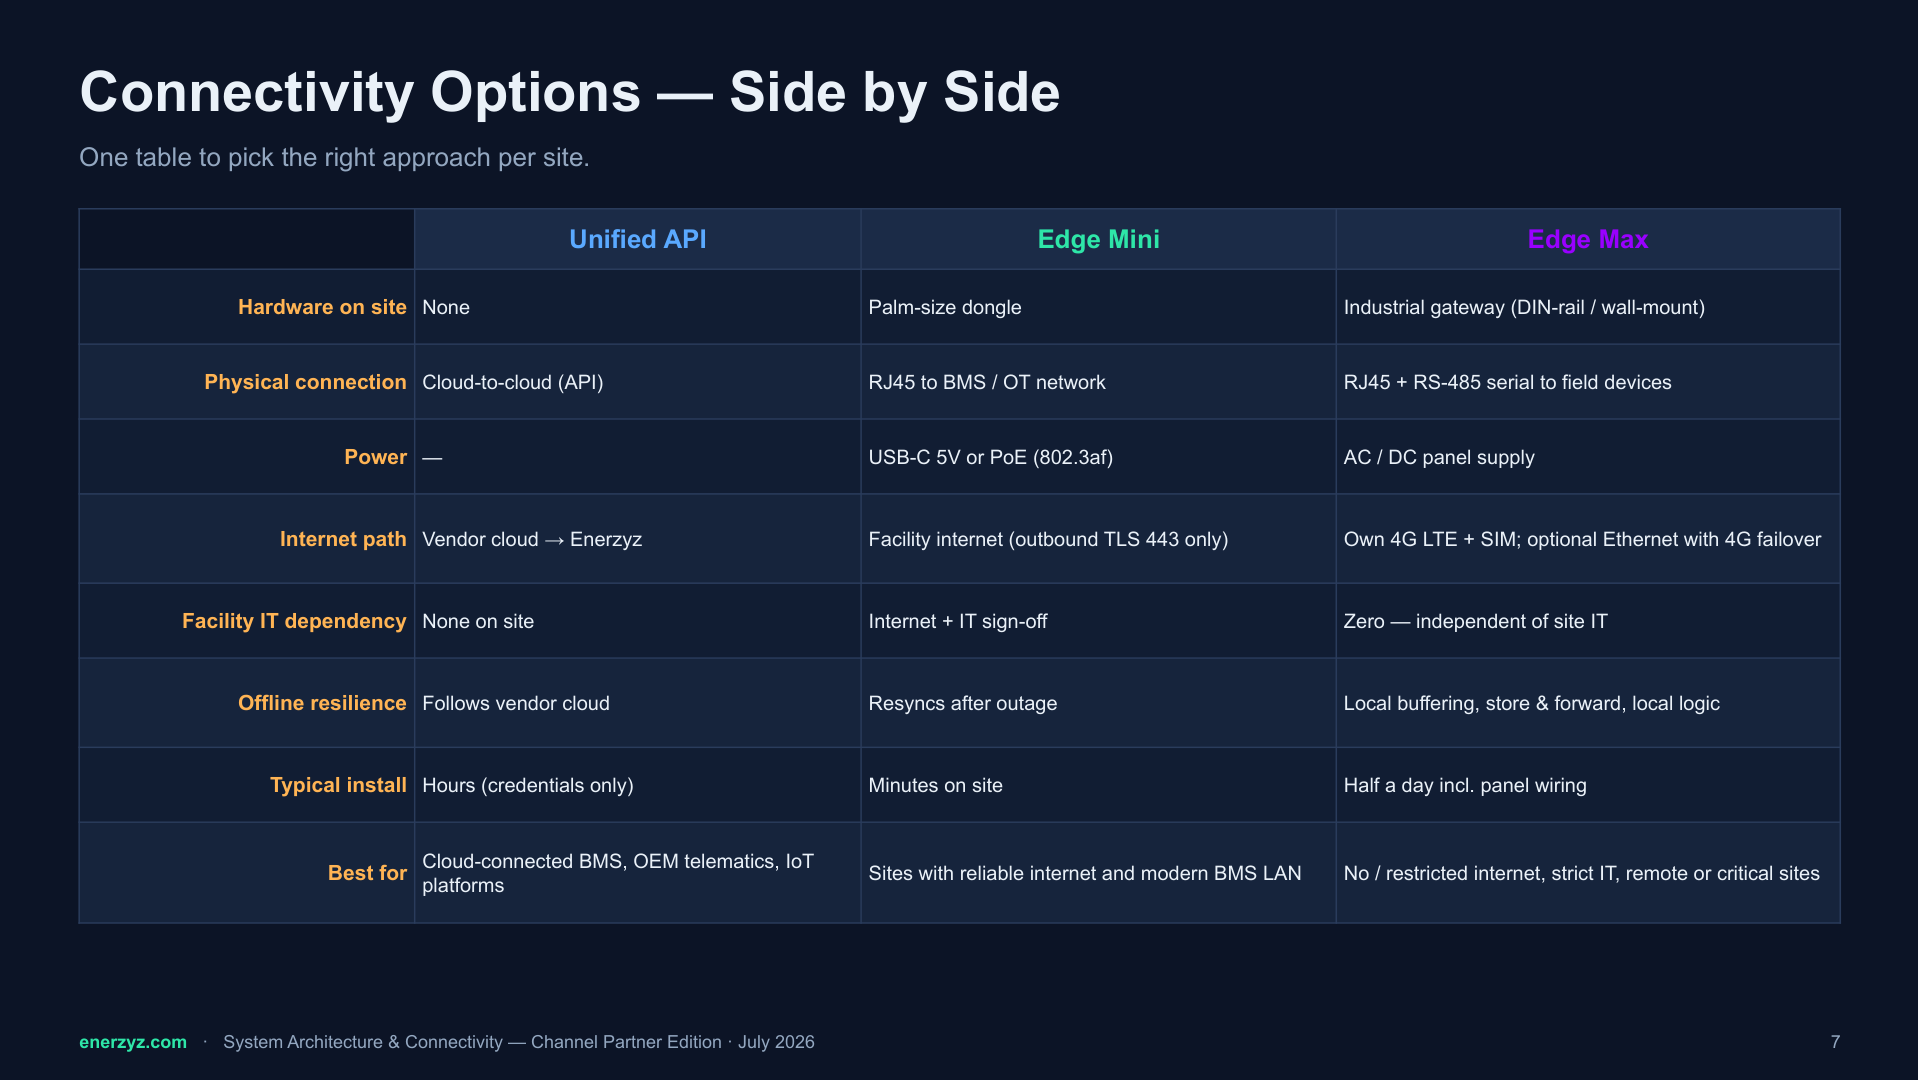
One table comparing the connection paths on the criteria a reviewer actually weighs: hardware on site, physical connection, power, internet path, facility IT dependency, offline resilience, typical install time and best fit. The table shows Unified API, Edge Mini and Edge Max. Unified API is typically live the same day, with no site visit; Edge Mini typically takes minutes on site; Edge Pro, which keeps your BMS network apart from the site LAN, typically under an hour; Edge Max typically half a day. Use this to scope the conversation your IT and engineering teams need to have.
Scroll the diagram sideways to read it in full.
Connection types and protocols
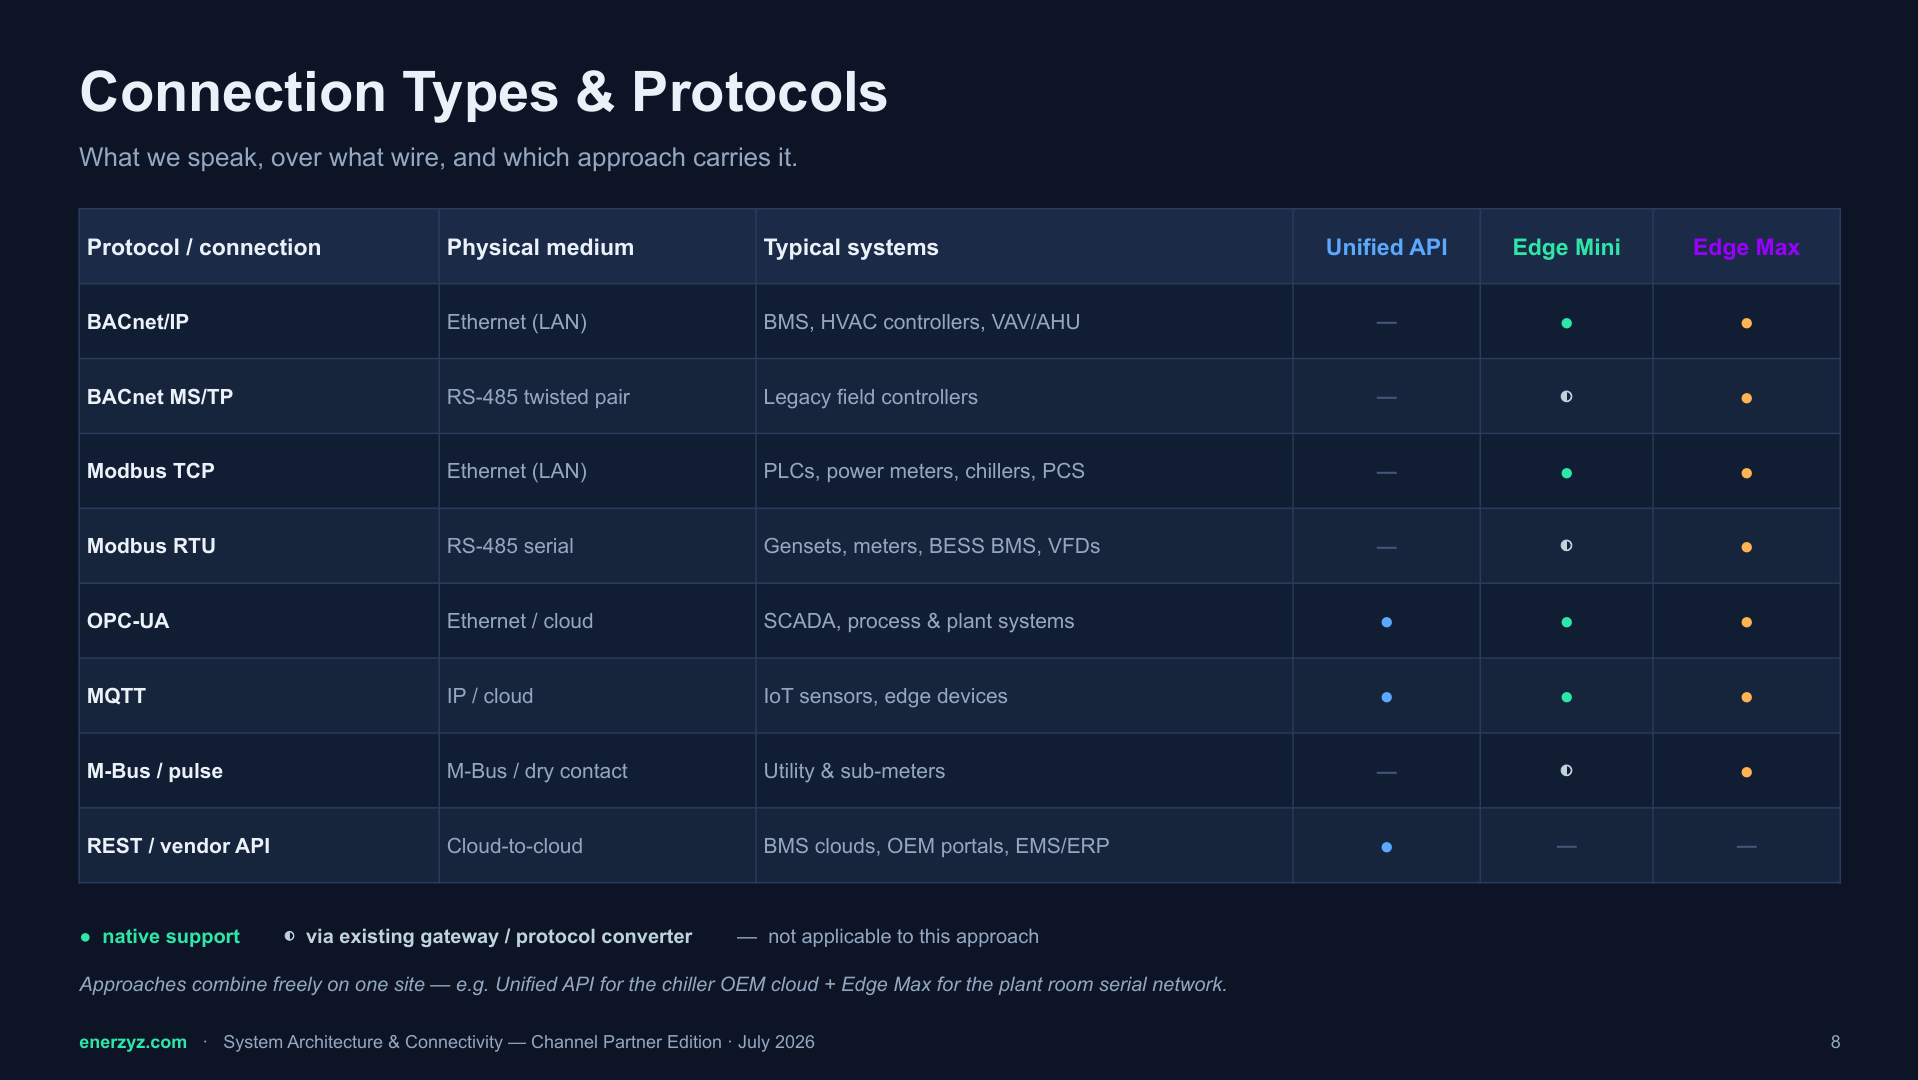
The protocol detail your controls engineer will want: which industrial protocols Enerzyz speaks, and over which transport. This is the page that answers “will it talk to what we already have” without a meeting. Enerzyz reads operational building telemetry only — equipment status, runtime, process variables and meter readings — and does not collect guest, patient or property-management personal data.
Scroll the diagram sideways to read it in full.
One architecture, thirteen verticals
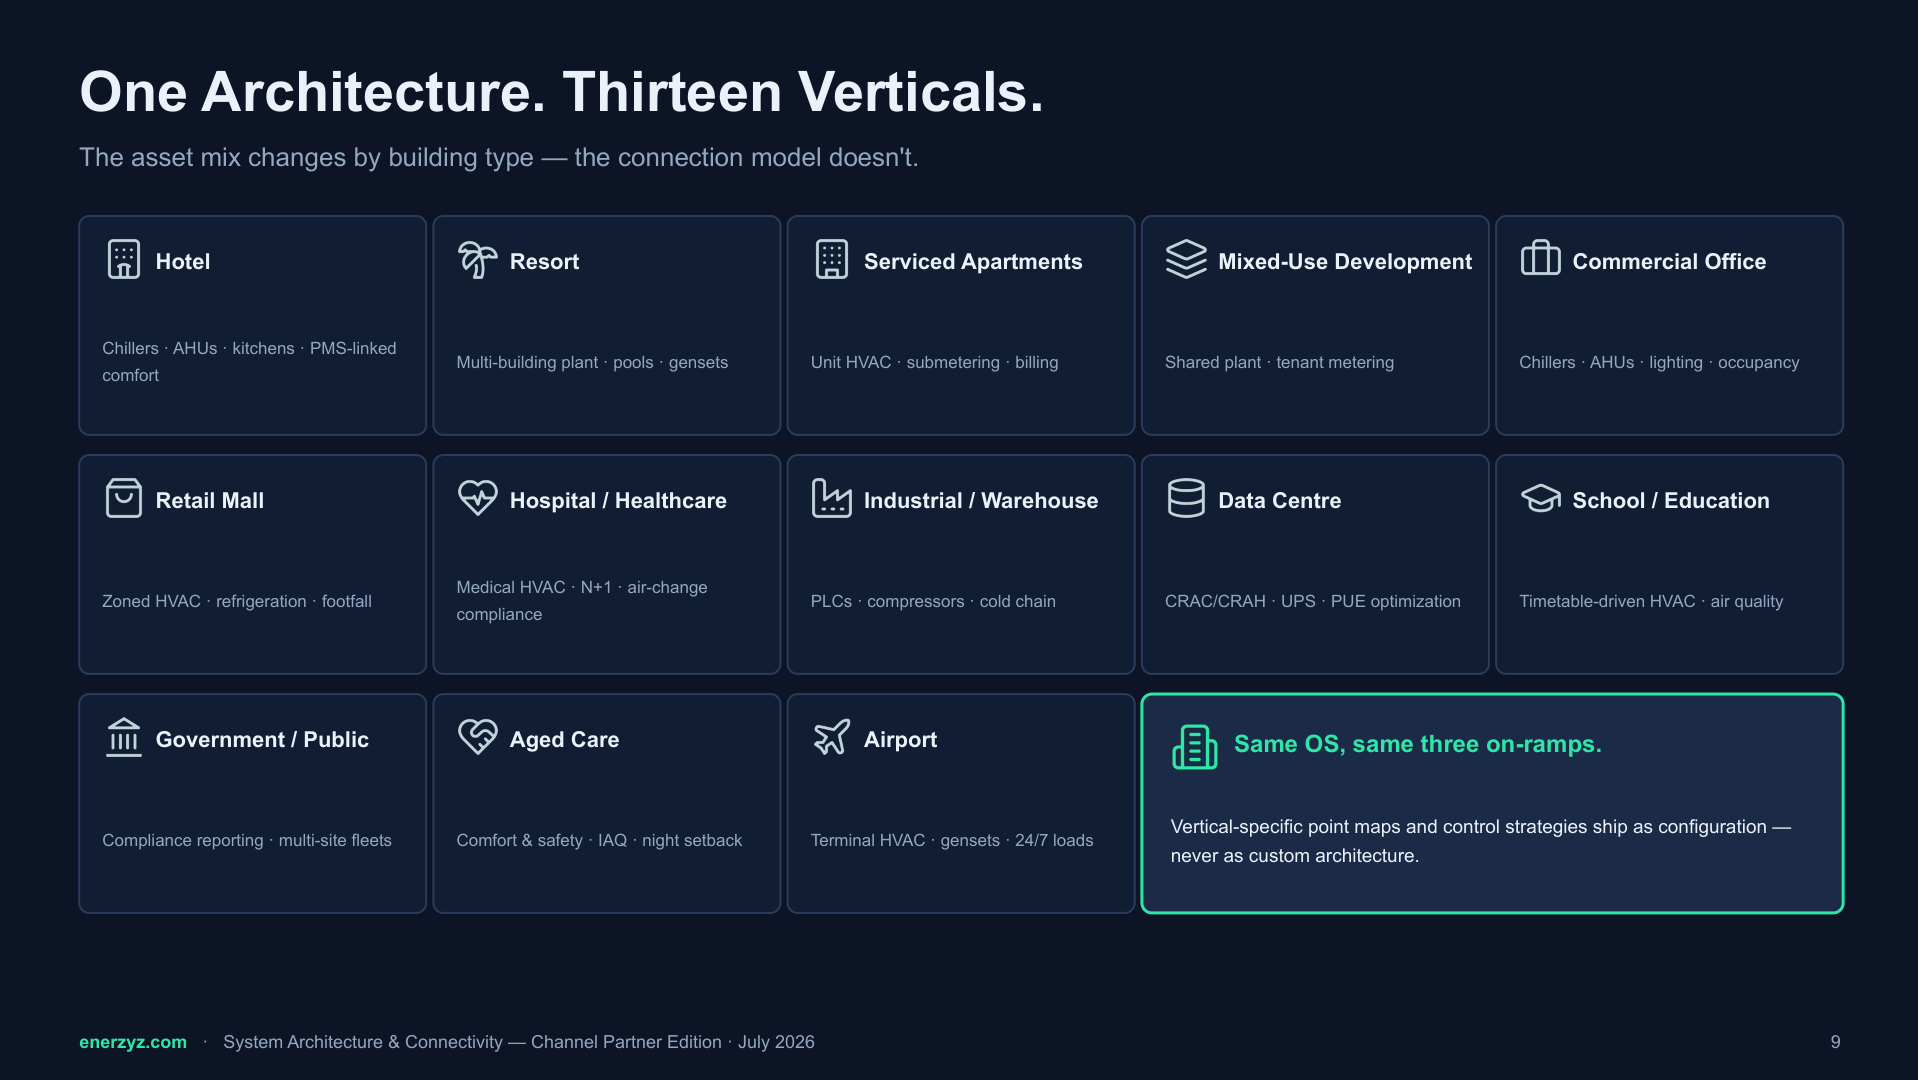
The same architecture applies across every facility type Enerzyz supports, from hotels and hospitals to data centres, cold storage and airports. What changes between verticals is the baseline methodology and which loads matter most, not the way the platform connects. If you operate a mixed portfolio, this is the diagram showing one integration approach covering all of it.
Scroll the diagram sideways to read it in full.
What this means for your network
Outbound-only connectivity
The Edge requires only outbound connectivity over port 443. No inbound rules are required at your firewall.
No inbound path from corporate IT
No Enerzyz Edge opens an inbound listening port or needs an inbound firewall rule, and no Edge forwards traffic between networks. Building-control traffic stays on your controls network. On the Edge Pro, which holds addresses on both the controls network and the site LAN, forwarding, routing and address translation between the two are disabled, so only outbound platform traffic crosses the site LAN. The connection model and network path for your site are stated in your order.
Mutual TLS, per-device certificates
TLS 1.2/1.3 with mutual authentication. Each device carries its own X.509 certificate, rotated on first cloud bind and annually thereafter.
Encryption in transit and at rest
Telemetry is encrypted end-to-end and signed; data at rest is encrypted with per-tenant key derivation in a customer-isolated store.
Your BMS stays authoritative
Where write-back is enabled, supervisory set-points are written through your BMS, which remains the authoritative control layer. Operators retain override authority at all times.
Single sign-on and audit trail
Console access is via your own identity provider (SAML 2.0 or OIDC) with role-based access control; privileged actions raise attributed audit events.
Certified and independently tested
Certified to ISO/IEC 27001:2022 and engineered with reference to IEC 62443, with periodic third-party penetration testing.
Data residency
An active-active multi-cloud back end across AWS Singapore, AWS US East (Northern Virginia) and Google Cloud Singapore. Unless a specific residency configuration is agreed, data may be processed in both Singapore and the United States; regions can be configured to meet residency requirements where supported.
The full Security & Data Protection White Paper is available on request, without an NDA. The third-party penetration-test summary and the Statement of Applicability are provided under NDA.